How to design a Rust library that records every file operation in an immutable, timestamped and verifiable chain to meet NIS2, GDPR and HIPAA requirements?
The turning point: from declarative compliance to evidentiary governance
NIS2 transforms the declarative requirement ("we have a policy") into an obligation of proof: every technical measure must be demonstrable. Management is responsible for justifying the presented artefacts. Every action must be accompanied by evidence attesting to its implementation, its retention over time, and the absence of tampering.
Expected qualities of evidence
- authenticity: identified source;
- integrity: SHA-256 or BLAKE3 hash;
- traceability: every step timestamped;
- reliable timestamping via TSA RFC 3161;
- attribution: actor identified via IAM;
- contextualisation: business metadata;
- availability throughout the legal retention period;
- long-term readability (JSON-LD, PDF/A);
- independent verifiability without vendor lock-in.
Evidence requested during an audit
| Type | Actionable evidence |
|---|---|
| Risk analyses | DPO-signed report, timestamped and hashed |
| Security policies | Signed PDF/A, timestamped, stored WORM |
| Cloud asset inventory | Signed JSON export, hashed and archived |
| Committee reports | Electronically signed minutes, WORM |
| Restoration tests | Execution logs with comparative checksums |
| SIEM technical logs | Timestamped immutable stream with signature |
Immutability as a trust mechanism
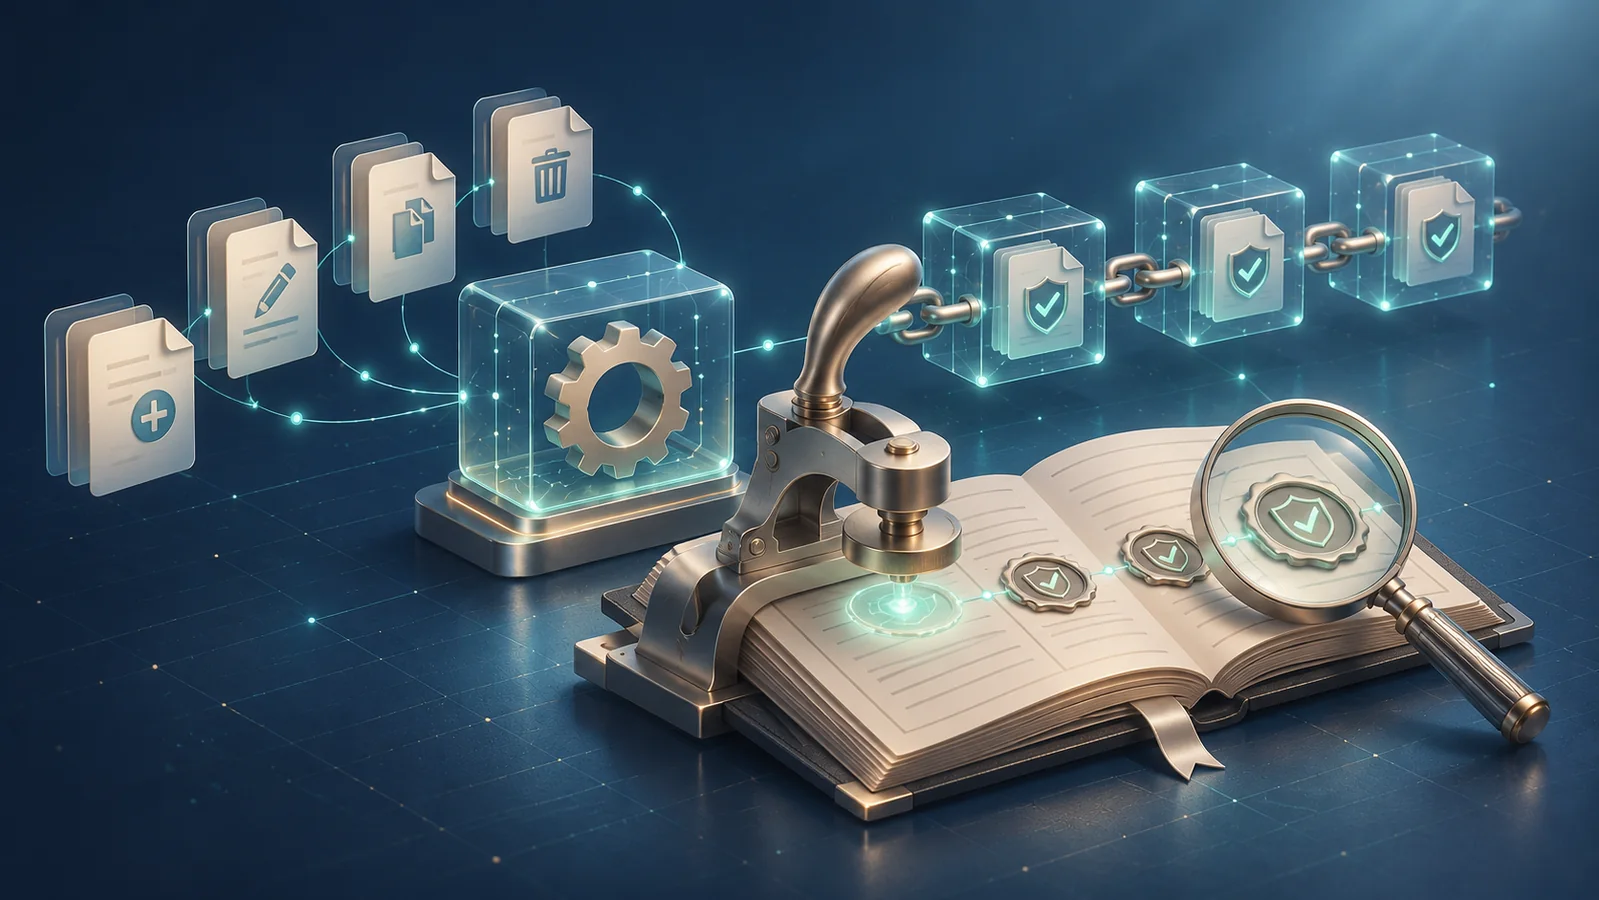
WORM storage (S3 Object Lock or Azure Immutable Blob) preventing any modification. Append-only logs. SHA-256 or BLAKE3 fingerprints detecting alterations. Event chaining (previous hash included in the next). Versioning creating a new immutable object upon each modification. Qualified timestamping via TSA. Centralised SIEM audit logs. Legal Hold and RBAC.
The Rust audit-cloud library
The library intercepts every cloud API call (PUT, GET, DELETE) and generates a structured JSON: ID, IAM operator, bucket, object key, size, checksum. The JSON and certificates are uploaded to an S3 Object Lock bucket (Compliance mode) with tags category=log and retention=7y. A daily verification recalculates the hashes; audit exports are produced as signed JSON-LD archives.
Pragmatic implementation for SMEs and mid-caps
- map applicable NIS2 obligations;
- define a proof register (simple PostgreSQL database);
- assign a data custodian per log category;
- specify signed JSON-LD format and 7 years of retention;
- automate via the Rust library integrated into the cloud SDKs;
- protect using S3 Object Lock, SSE-KMS and restrictive IAM.
Limits that should not be obscured
- false immutability if the hashing process is flawed;
- source quality is paramount;
- GDPR conflict (right to erasure) vs NIS2 requiring analysis;
- local vs qualified timestamping: different legal weight.
Further reading
Related links:
Read the Challenges article on KARL →