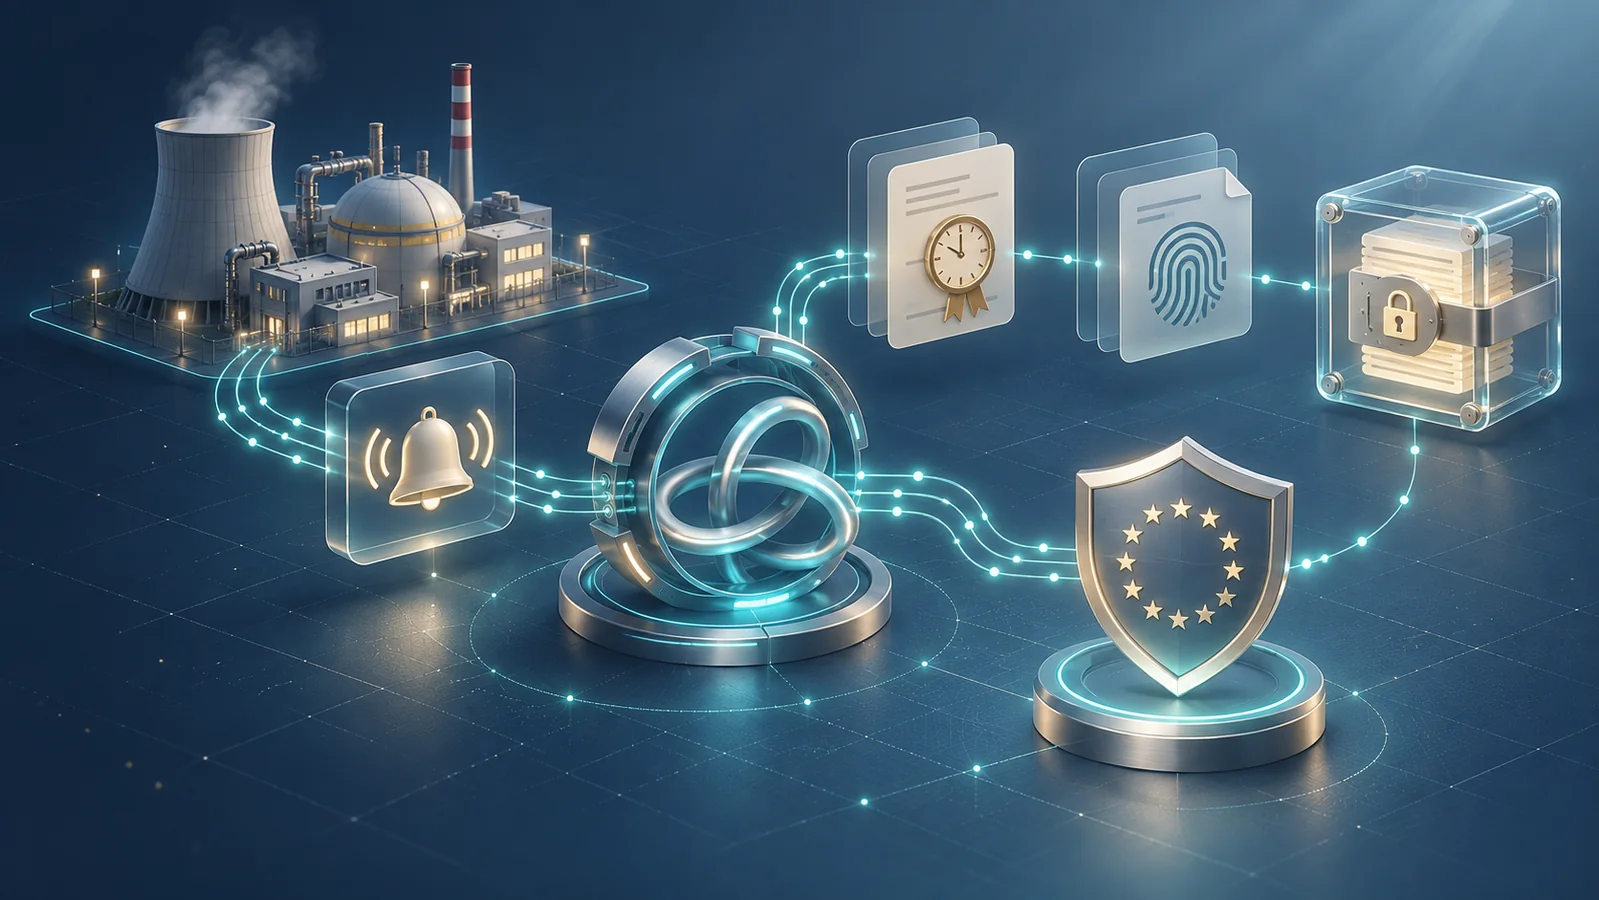
Tokio supports real-time alerting pipelines with the immutable legal traceability required by NIS2.
Evidence for each asynchronous alert
- authenticity: each alert receives a digitally signed UUID v4;
- integrity: JSON payload hashed via SHA-256 prior to broadcast;
- traceability: Tokio maintains execution order via logged task IDs;
- timestamping: hash sent to the TSA, signed certificate returned;
- attribution: logger includes the service, K8s container ID, and Git commit;
- contextualisation: source IP metadata, sensor type.
Essential crates
| Crate | Role |
|---|---|
| tokio (1) rt-multi-thread | Multi-threaded asynchronous runtime |
| serde / serde_json | JSON-LD serialisation |
| uuid (1) v4 | Unique identifiers |
| sha2 | SHA-256 hash calculation |
| ring / ed25519-dalek | Digital signature (EdDSA) |
| zeroize | Secure erasure of memory secrets |
| reqwest | Sending the hash to the TSA |
| aws-sdk-s3 | Immutable upload to S3 Object Lock |
What an auditor will seek to verify
- existence of a unique UUID v4 associated with each alert;
- presence of a SHA-256 hash signed by a qualified TSA;
- storage of the artefact in a WORM mode bucket;
- use of zeroize ensuring the erasure of private keys;
- traceability of Tokio tasks (task-id, thread-id) within the log.
Chain of custody for an alert
Tokio receives the event via TcpListener::accept and transforms it into an Alert struct. The source_id (sensor UUID) and commit_git fields are injected. Instant::now() synchronised via NTP, SHA-256 hash sent to the TSA, certificate retrieved. The SHA-256 of the payload + metadata = alert_hash. Upload to an S3 Object Lock bucket (retention=7y) with tags type=security_alert and criticality=high. Restrictive IAM access control.
Limitations not to be obscured
- immutability does not eliminate false alerts generated at the source;
- primordial source quality;
- local vs qualified timestamping: differing legal weight;
- significant cost of WORM and TSA services for SMEs.
Further reading
Further reading:
Read the Challenges article on KARL →
KARLStorage that remembers.