On 14 March 2026, an underwriting agent declines a credit application. Eight months later, the credit ombudsman asks on what basis. The question is not whether the agent worked properly: it is what the agent actually had in memory that day, and whether the company can demonstrate it to a third party who has no reason to trust its servers.
The scenario is fictional but representative of the requests legal and compliance teams receive today. It shows, screen by screen, how KARL Core answers that question: state versioning, a temporal graph of objects, governed retrieval and a sealed Evidence Pack.
The setting: Kelenia Crédit and the ARIA agent
Kelenia Crédit is a consumer lending institution. Since 2025, part of its underwriting has been delegated to ARIA, an agent that pre-qualifies applications, applies the credit policy in force and drafts a rationale when a file is declined. ARIA runs on KARL Core: every file, every policy version and every decision is kept as a governed resource, never as an ordinary file.
On 14 March 2026, ARIA reviews file DOS-2026-0847 for Mr Reyval and issues a refusal, justified by a debt-to-income ratio deemed excessive under the consumer credit policy then applicable. Eight months later, the customer refers the matter to the credit ombudsman. Kelenia's legal department must answer a precise question: what exactly did ARIA know, and on what basis did it decide?
The compliance team’s KARL MX workflow rebuilds that evidence, screen by screen, from the file’s history to the sealed package handed to the ombudsman.
The foundation: the Memory Layer
In KARL Core, a credit file is not a single document edited in place. It is a persistent identity — dossier_credit / DOS-2026-0847 — where every change produces a new state, dated, signed and retained. Nothing is overwritten: the version received in February, the version completed after supporting documents, and the version carrying ARIA's decision all coexist in the same history.
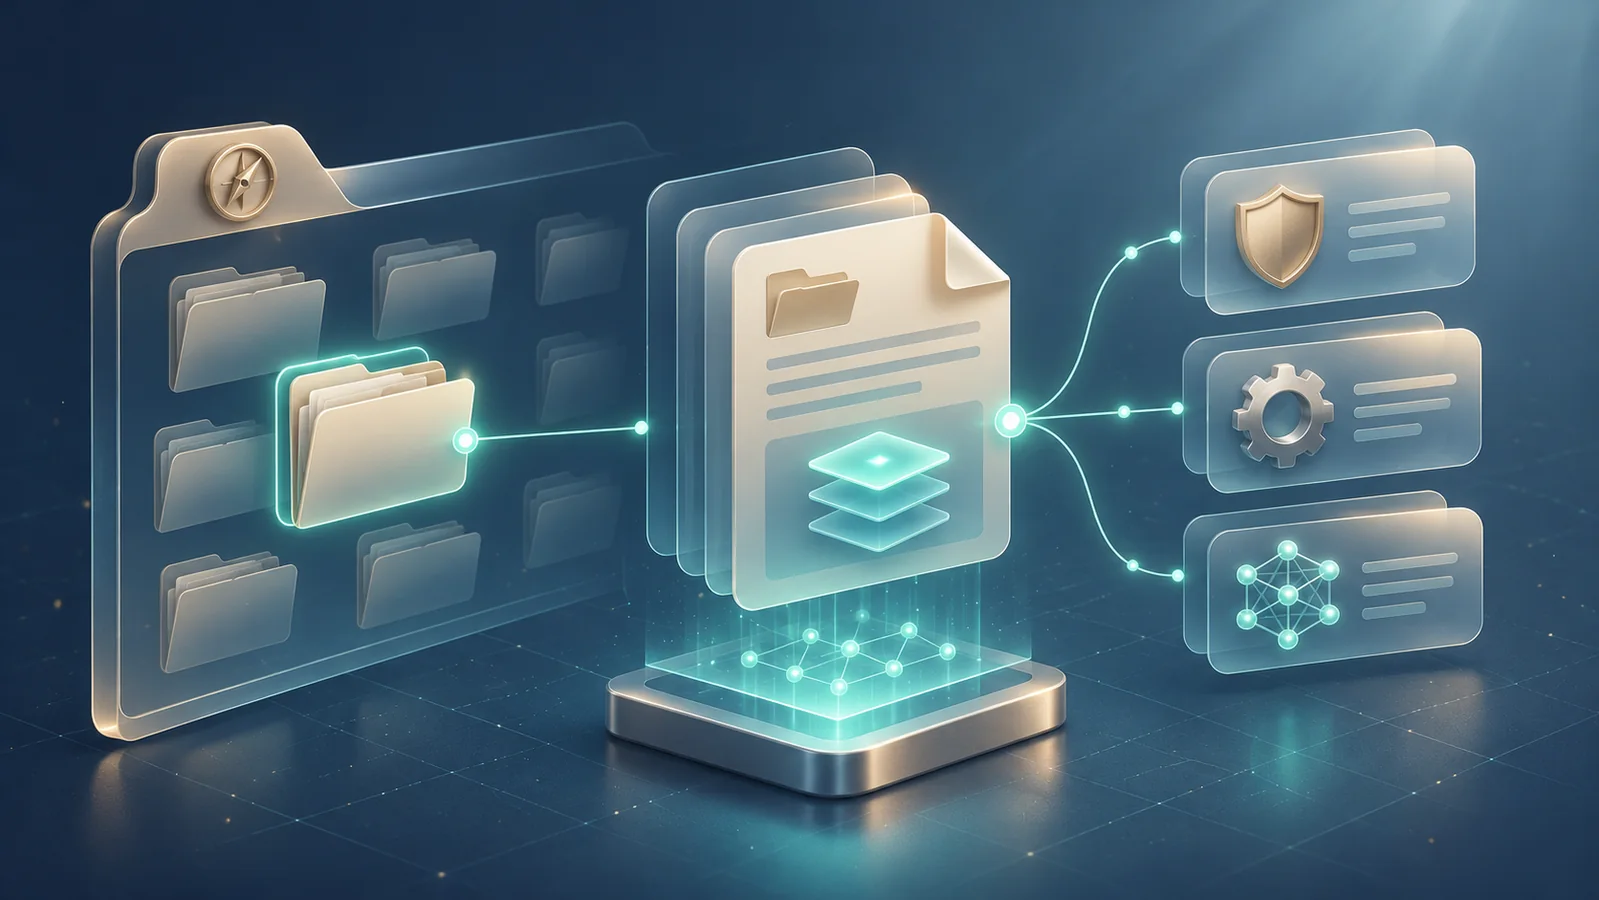
The Memory Layer tab then rebuilds, for that specific file, all of its version layers and the journal events that explain them: who acted, when, and what type of operation was logged. Nothing is simulated — every line comes from a verified read of Core.
Links between objects: the temporal graph
A decision never stands alone. It relies on a precise version of the credit policy, on the state of the file at the moment it was issued, and on the very execution of the agent that produced it. The temporal graph makes those links visible and verifiable: every arrow references an exact state, never just a name displayed on screen.
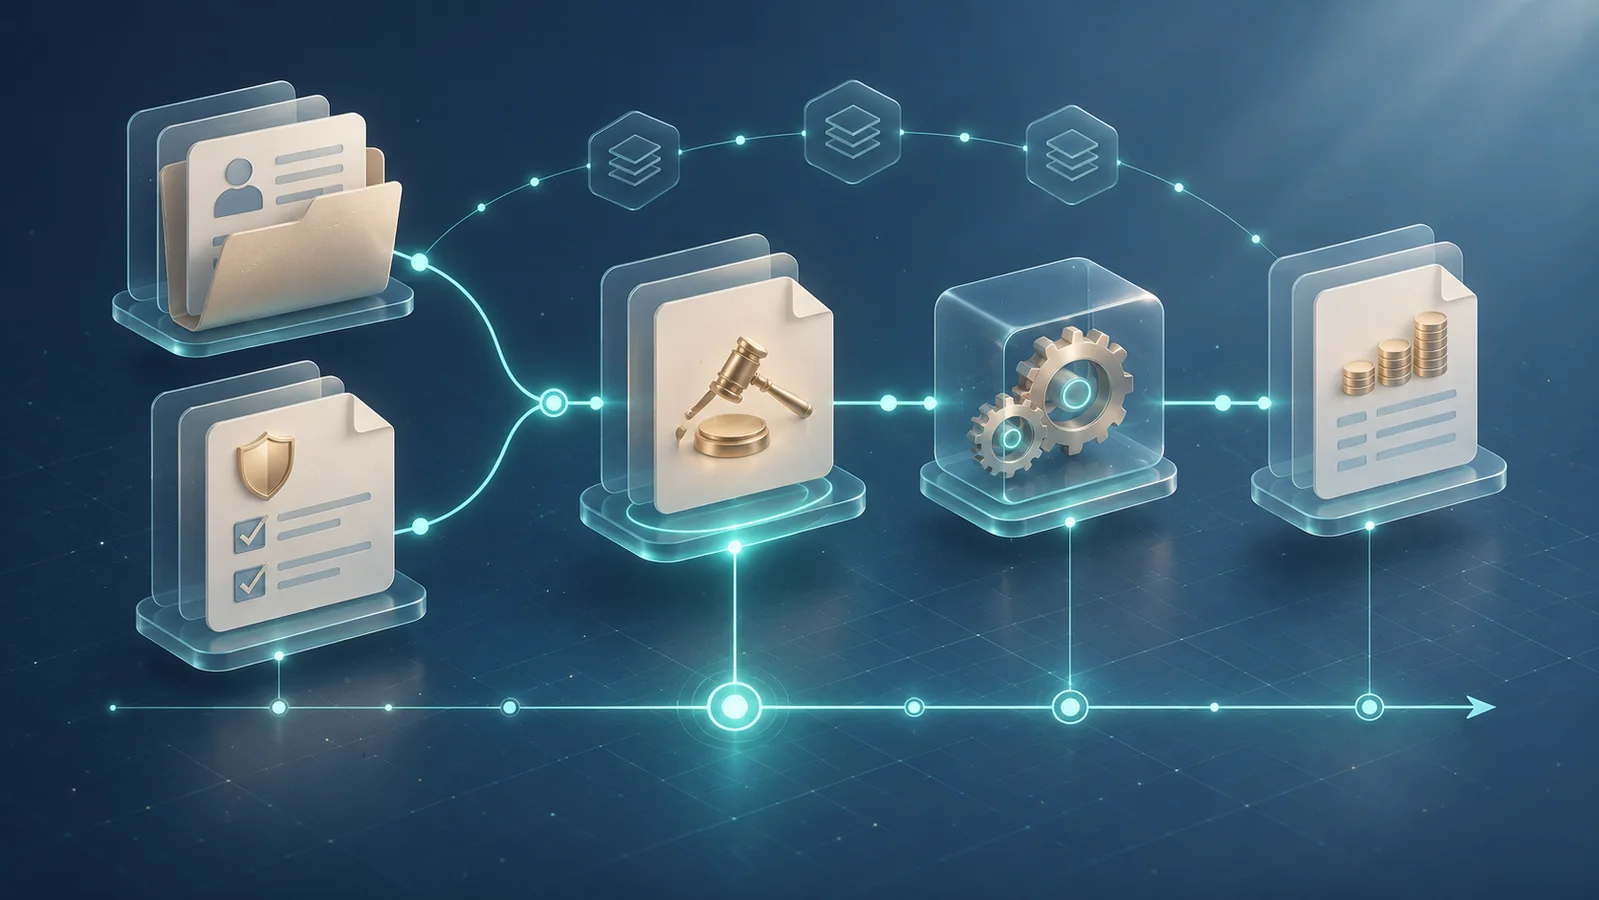
It is this structure of links, rather than a plain text log, that answers the ombudsman's question precisely: which policy, which file, which execution.
What ARIA had in memory: governed retrieval
The compliance team's question is direct: which documents did ARIA rely on to justify the refusal? Governed retrieval in KARL Core never returns a plain text excerpt: every result cites an exact resource and version — never the latest available version substituted for what was actually read.
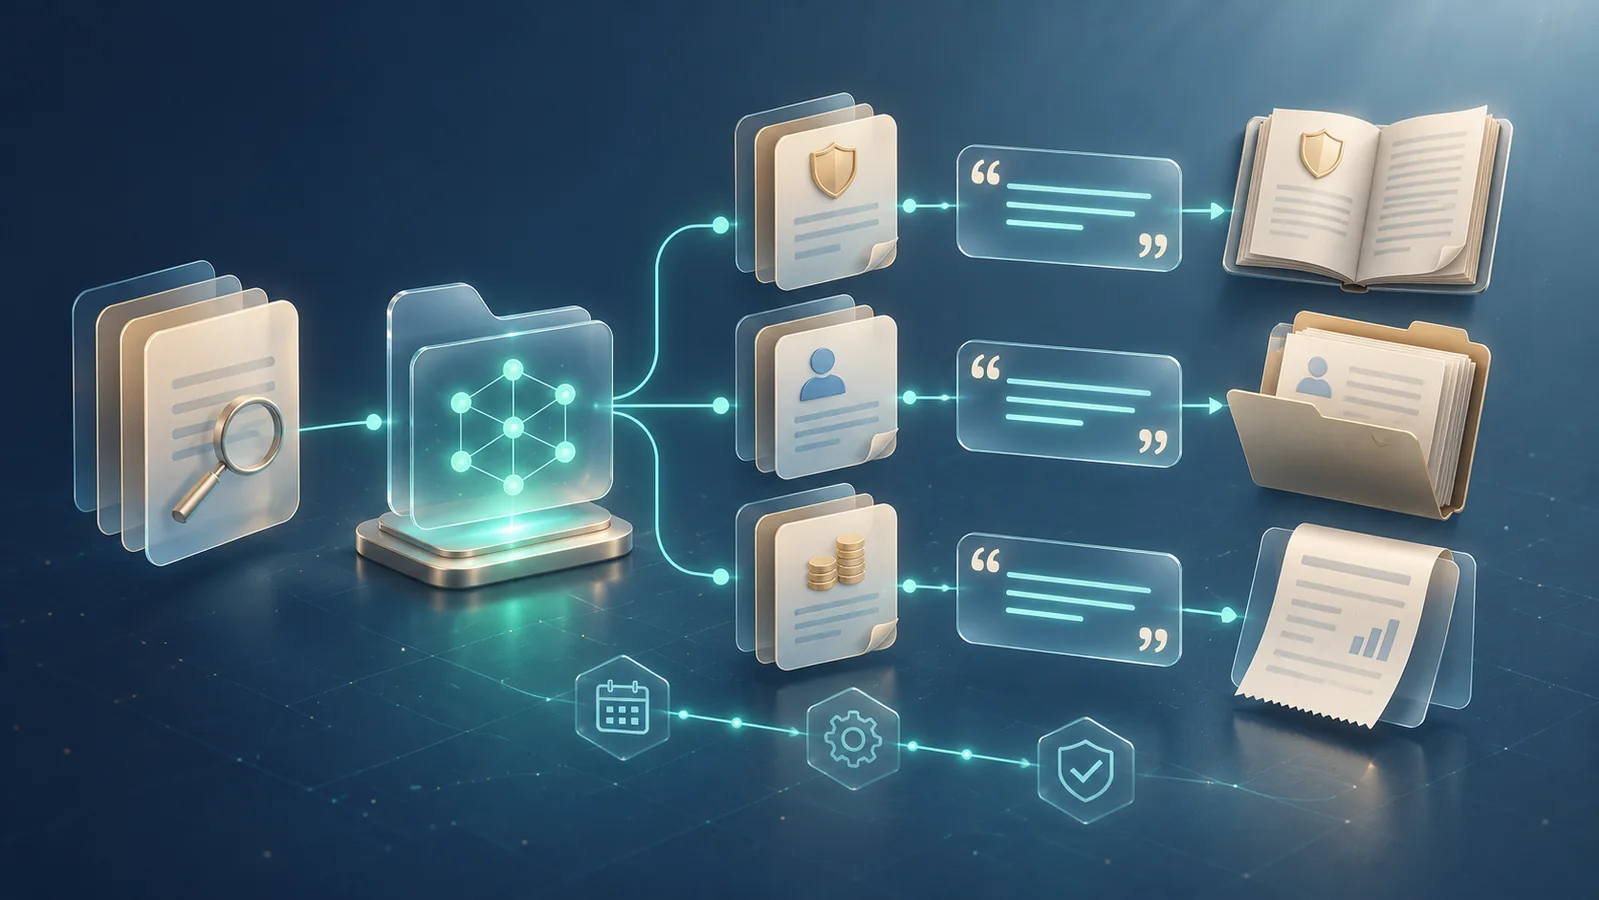
At this point the compliance team can already answer: the file, the policy and the supporting documents are identified, version by version. What remains is to produce evidence that Kelenia Crédit can hand to a third party who does not trust its servers.
The trigger: a complaint and a request for proof
The credit ombudsman asks Kelenia Crédit to demonstrate, in a verifiable and dated form, which data and which policy the decision of 14 March 2026 was based on. A screenshot or a courtesy export is not enough: the evidence must remain valid if contested, and verifiable without having to trust the Kelenia server. That is precisely the purpose of an agent_memory Evidence Pack: sealing, at a specific instant, the exact state of the resources that fed an agent's decision.
The sealed answer: the Evidence Pack
The KARL MX Evidence Pack wizard guides the compliance team through five steps. The first is a read-only analysis: no writes, no side effects. It freezes a capture boundary — a common journal sequence — and announces the exact inventory the export would produce: 36 entries for 21.1 KiB in this case, with 2 typed omissions tied to the selected audit profile.
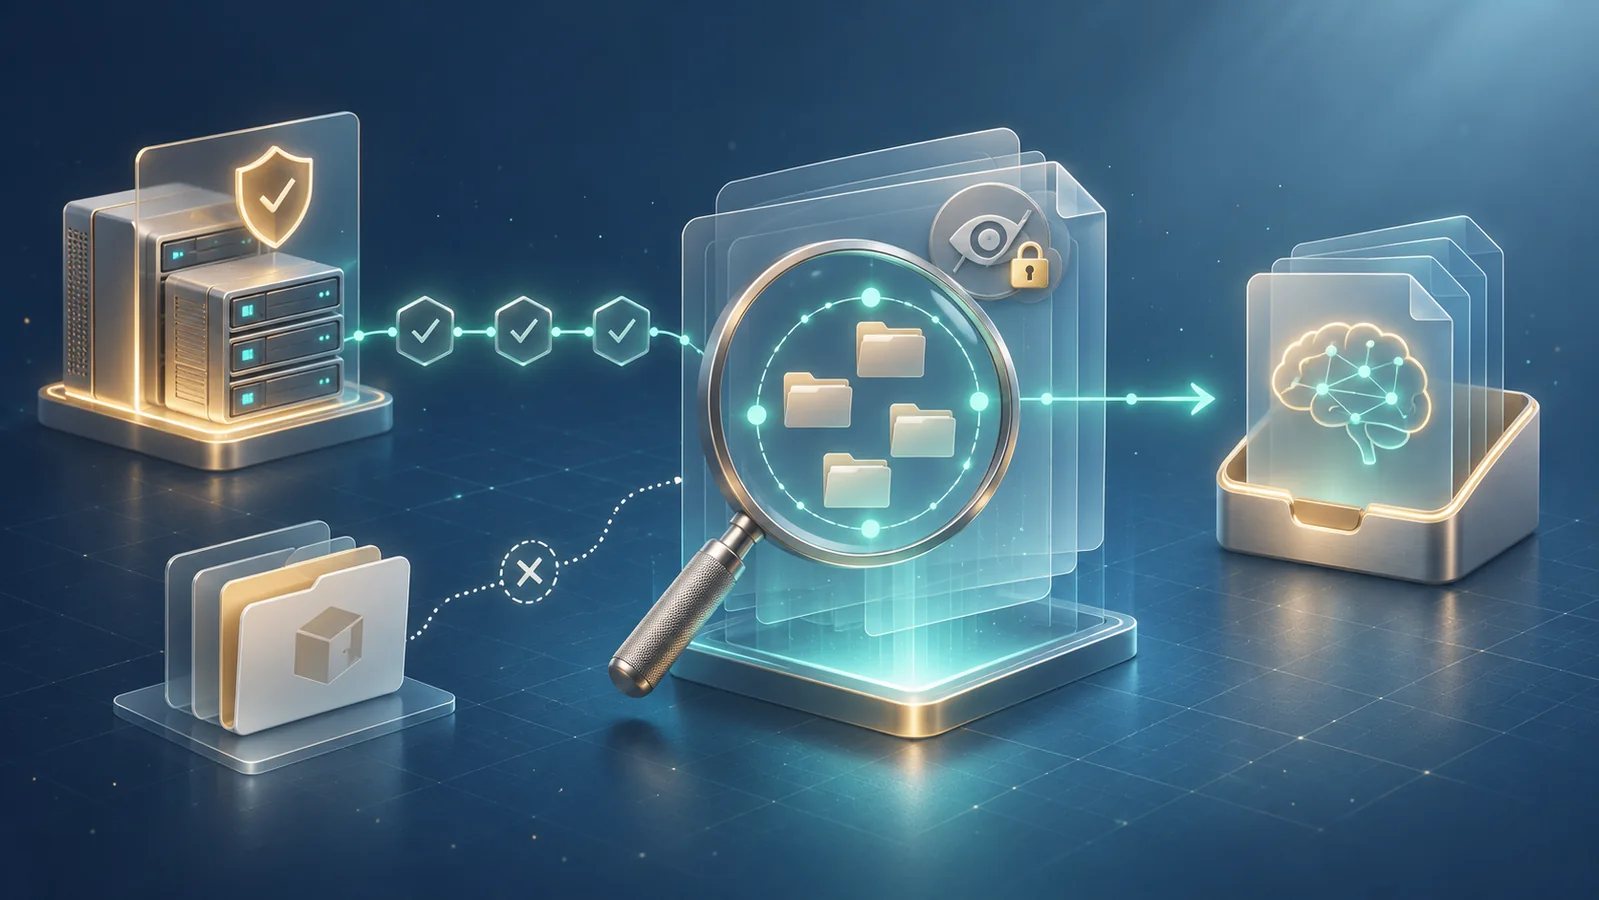
Once the analysis is validated, the export produces a sealed pack: every file is written then hashed, the whole is signed on behalf of the producing tenant, and an identifier derived from the content (bundle_id) identifies it uniquely. The karl.evidence-pack.v1 manifest becomes the identity document of the pack, and a producer self-check runs before any handover.
What Kelenia Crédit hands to the ombudsman
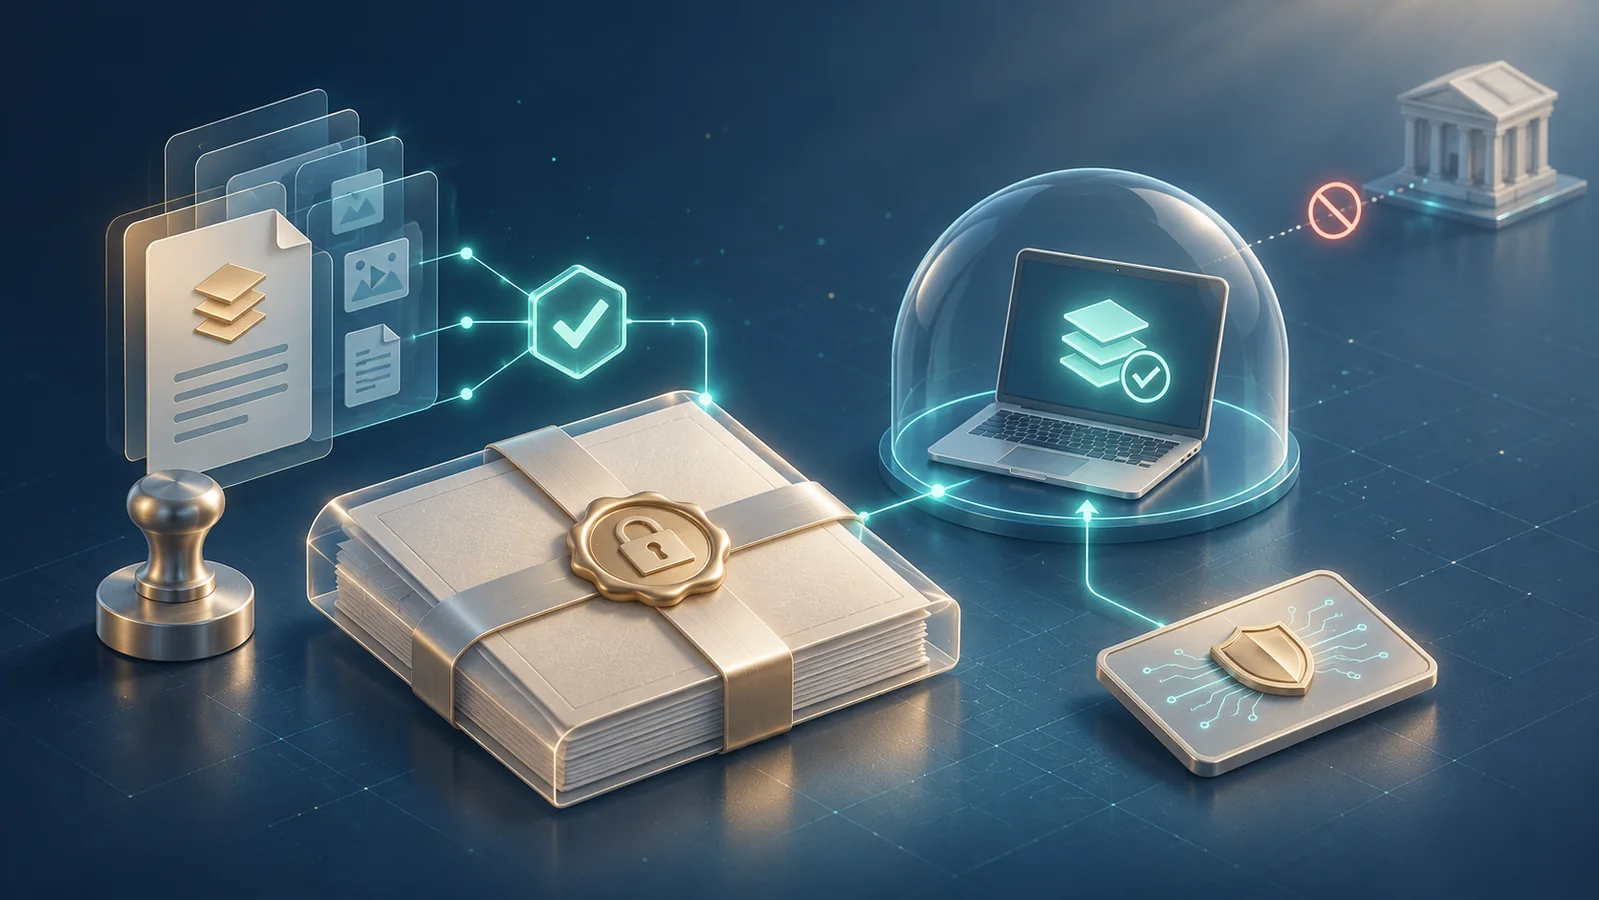
The deliverable is a portable directory containing the sealed manifest and every file together with its size and SHA-256 digest. The ombudsman — or their technical expert — runs the independent verification tool themselves, on a machine that has never had access to Kelenia Crédit servers. The verdict depends on no statement from the company: it depends only on the content received and on the trust root transmitted out of band.
Kelenia Crédit can therefore answer the complaint with a case file that documents, without after-the-fact interpretation, the exact version of its credit policy, the exact state of the file and the precise execution of its agent at the moment of the decision.
What it changes, function by function
| Function | Challenge | Answer provided |
|---|---|---|
| Legal and litigation | Answer a complaint or an ombudsman with evidence that withstands challenge | Sealed, signed pack, verifiable without depending on the company's server |
| Compliance and AI governance (GDPR, AI Act) | Demonstrate, decision by decision, which data and which model were used | Exact citations (kind, stable_id, version) and declared model, with no approximate reconstruction |
| Customer relations and mediation | Shorten the handling time of a dispute | Reconstruction in a few screens instead of a manual search across systems |
| IT department | Avoid exposing production data or access keys to a third party | Offline export, verifiable without a connection or Kelenia Crédit credentials |
| Executive management | Limit the reputational and regulatory risk of a contested automated decision | Dated and signed traceability, enforceable, available before the dispute escalates |
In short
The DOS-2026-0847 scenario illustrates four layers of a single foundation: the Memory Layer retains every state without ever overwriting it, the temporal graph connects those states to each other, governed retrieval finds and cites precisely what an agent read, and the Evidence Pack turns that memory into sealed evidence Kelenia Crédit can hand to a third party with confidence.
The same mechanism applies to needs other than agent memory: justifying a decision, proving a data purge, certifying a delivery or organising the reversibility of a contract. The foundation stays the same; only the pack_type changes depending on the question to be answered.
Quick glossary
| Term | Meaning |
|---|---|
| Memory Layer | Complete, immutable history of the versions of a resource and of the journal events |
| Temporal graph | Representation of the verifiable links between several resources within the same scope |
| Governed retrieval | Search where every result cites an exact resource and version, never substituted |
| Producing tenant | Trust identity (signature chain) that seals an Evidence Pack, distinct from the exported project |
| bundle_id | Identifier derived from the sealed content: any change to the content changes the identifier |
Kelenia Crédit, file DOS-2026-0847 and the ARIA agent are fictional. The screenshots come from the KARL MX interface running on a demonstration dataset: the mechanism shown is real, the data is not.