The European NIS2 directive shifts cybersecurity from a declarative approach to an evidence-based one. Organisations must now demonstrate, in a verifiable and cryptographically traceable manner, that every security measure has been decided upon, executed, and preserved.
An incident that could have been avoided
Educational scenario (fictitious). Imagine a company whose production server is compromised. Service is restored, but during an audit, no formal evidence proves that backup measures had been tested: the logs stored on a network share are partially corrupted. Lacking probative evidence, the organisation cannot demonstrate that its measures were in place and operational—a situation which, depending on the context, may lead to compliance requests from the competent authority.
This episode illustrates the transition from declarative compliance ("we have a backup policy") to a requirement for immutable proof ("we demonstrate that the backup was performed, tested, and preserved without alteration").
From declarative compliance to evidence-based governance
Directive (EU) 2022/2555 (NIS2) introduces, for essential and important entities:
- the obligation to implement technical and organisational measures appropriate to the risk level;
- risk lifecycle management including periodic analyses;
- an incident process with notification to the competent authority within 24 hours;
- the establishment of a governance organisation with management accountability.
NIS2 mandates appropriate risk management measures and a structured process for notifying significant incidents. Log retention periods and timestamping mechanisms are not universally fixed by the directive: they must be determined according to the applicable national transposition texts, the sector concerned, the nature of the evidence, and other regulations in force (GDPR, sectoral requirements, etc.).
The essential attributes of actionable evidence
| Attribute | Definition | Why it is required |
|---|---|---|
| Authenticity | The data source is identifiable and legitimate | Ensures that the document does not originate from an unauthorised actor |
| Integrity | The content has never been altered since its creation (cryptographic hash) | Prevents post-hoc manipulation |
| Traceability | Recorded chain of generation, modification, and consultation | Allows each step to be attributed to an actor |
| Trusted Timestamping | Certified timestamp (Qualified TSA) | Prevents backdating and confirms the chronology |
| Attribution | Identity of who produced or validated the document | Facilitates legal accountability |
| Availability | Guaranteed access throughout the retention period | The auditor must be able to consult at any time |
| Long-term readability | Sustainable format (PDF/A, JSON-LD) and migration | Prevents technological obsolescence |
| Independent verifiability | A third party can verify without relying on the creator | Strengthens trust in the evidence system |
Immutability protects content from the moment it is recorded; it does not guarantee that it was correct initially. A document falsified before being sealed remains incorrect. Governance of initial sources is therefore indispensable.
Evidence expected by NIS2 auditors
| Domain | Example of immutable evidence | Gap compared to a simple document |
|---|---|---|
| Risk analysis | Signed and timestamped PDF report, SHA-256 fingerprint stored in WORM | A shared spreadsheet shows neither validation nor precise date |
| Security policy | WORM version with formal timestamped approval | A Word copy can be modified without a trace |
| Asset inventory | Signed JSON export of the CMDB, daily archiving | Manual Excel list without history |
| SIEM logs | Append-only stream to WORM, millisecond timestamping | Local logs that can be truncated or altered |
| Restoration tests | Automated report + hash of restored data | Screenshot without proof of consistency |
| Incident notification | Tracked notification with acknowledgement of receipt and timestamping | Internal note editable at a later date |
The limitations of traditional documentation practices
- shared folders allowing deletion or modification without logging;
- manual renaming erasing the link to the approved version;
- spreadsheets that do not preserve differences between versions;
- logs retained for only 30 days whereas NIS2 requires several years;
- screenshots lacking system context or reliable timestamping;
- administrator accounts capable of altering evidence without leaving a trace;
- evidence fragmented across multiple departments and tools.
Immutability as a trust mechanism
| Mechanism | Technical principle | NIS2 contribution |
|---|---|---|
| WORM (Write-Once-Read-Many) | Medium preventing any rewriting after initial write | Guarantees the non-alteration of deposited content |
| Append-only logs | New entries added to the end only | Preserves an unalterable chronological stream |
| SHA-256/SHA-3 fingerprints | Unique hash calculated upon creation | Detects any modification, however slight |
| Hash chain | Each entry incorporates the hash of the previous one | Makes any insertion or deletion detectable |
| Merkle Tree | Fingerprints combined in pairs up to a single root | Verification of an entire batch in a single calculation |
| Qualified Timestamping (TSA) | Timestamp issued by an eIDAS qualified provider | Enhanced legal probative value |
| Legal Hold | Suspension of deletion during proceedings | Prevents the loss of relevant evidence |
Chain of custody
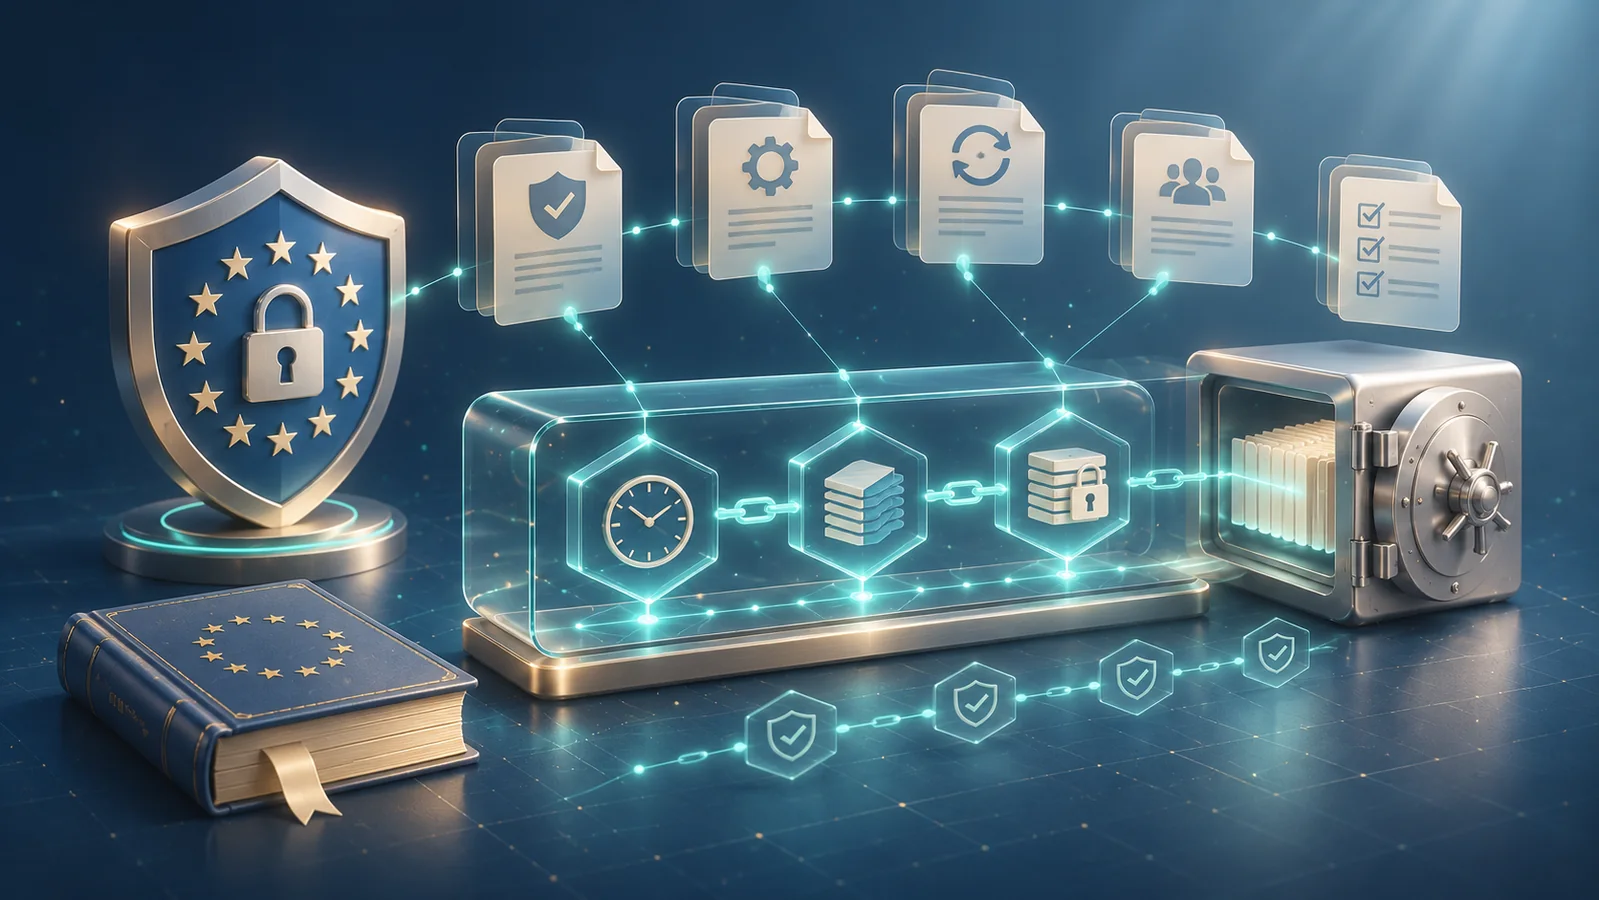
Each piece of evidence must undergo the same stages: Creation → Identification (UUID) → TSA Timestamping → SHA-256 Hashing → WORM Deposit → Classification → RBAC Access Control → Retention → Periodic Verification → Audited Consultation → End of Life or Legal Archiving.
By recording every link in the chain, the organisation creates an evidence register that can be leveraged within minutes during an audit.
Pragmatic implementation for SMEs and Mid-caps
- map applicable obligations and risks;
- create a centralised evidence register (category, source, duration, owner);
- appoint a data custodian per category (logs, backups, policies...);
- automate collection: cron scripts that hash then push to S3 Object Lock;
- enable qualified timestamping for each major artefact;
- schedule monthly hash verifications and quarterly restoration tests;
- simulate an internal audit every quarter to validate responsiveness.
What KARL delivers
KARL natively provides the building blocks required by NIS2: automatic versioning of every object, configurable WORM immutability, precise timestamping, full access traceability, and one-click auditable export. The chain of custody is no longer a project to be built, but a property of the storage itself.
Disclaimer: this article is an editorial analysis for informational purposes and does not replace legal advice. Specific requirements (retention periods, timestamping, scope) depend on national transposition laws and the relevant sector. KARL is a product published by StratoFoundry; references to this product are for commercial purposes.
Find out more
To understand how temporal storage becomes a foundation for compliance:
Read the Challenges article on KARL →