How to build a chain of custody for evidence that meets NIS2 legal requirements by combining immutable storage, SHA-256 hashing and qualified timestamps?
From declaration to proof
NIS2 mandates irrefutable traceability. Every security action must be logged with a reliable timestamp, authenticated, and retained for the legal duration (5 to 7 years). No specific technology is mandated, but the evidence must be immutable, independently verifiable, and legally admissible.
Essential attributes of evidence
- authenticity: identifiable and legitimate source;
- integrity: SHA-256 hash detecting any alteration;
- traceability: every step logged with identity;
- qualified timestamping via TSA RFC 3161;
- attribution: clearly identified author or system;
- contextualisation through business metadata;
- availability throughout the legal retention period;
- long-term readability (sustainable formats PDF/A, JSON-LD);
- retention control via Legal Hold;
- independent verifiability by a third-party auditor.
Immutability alone does not guarantee accuracy; it protects content after recording. The quality of the initial source remains indispensable.
Limitations of standard documentation practices
- shared folders lacking reliable versioning;
- manual renaming causing loss of temporal links;
- editable documents without hashes or signatures;
- evidence scattered across multiple services;
- logs retained for too short a period;
- screenshots lacking metadata or context;
- untested backups;
- administrator accounts capable of altering audit trails.
Immutability as a trust mechanism
| Mechanism | Contribution to NIS2 |
|---|---|
| WORM (S3 Object Lock, Azure Immutable Blob) | Rejection of any rewrite after initial commit |
| Append-only logs | Additions only at the end of the file, unalterable sequence |
| SHA-256 fingerprints | Immediate detection of any tampering |
| Merkle chaining | Global batch verification in a single calculation |
| Qualified timestamping (TSA RFC 3161) | Legal probative value before authorities |
| Versioning | Preserves every iteration with ID and timestamp |
| Legal Hold | Suspension of deletion during an investigation |
| RBAC + separation of duties | Limits the risk of internal tampering |
Chain of custody
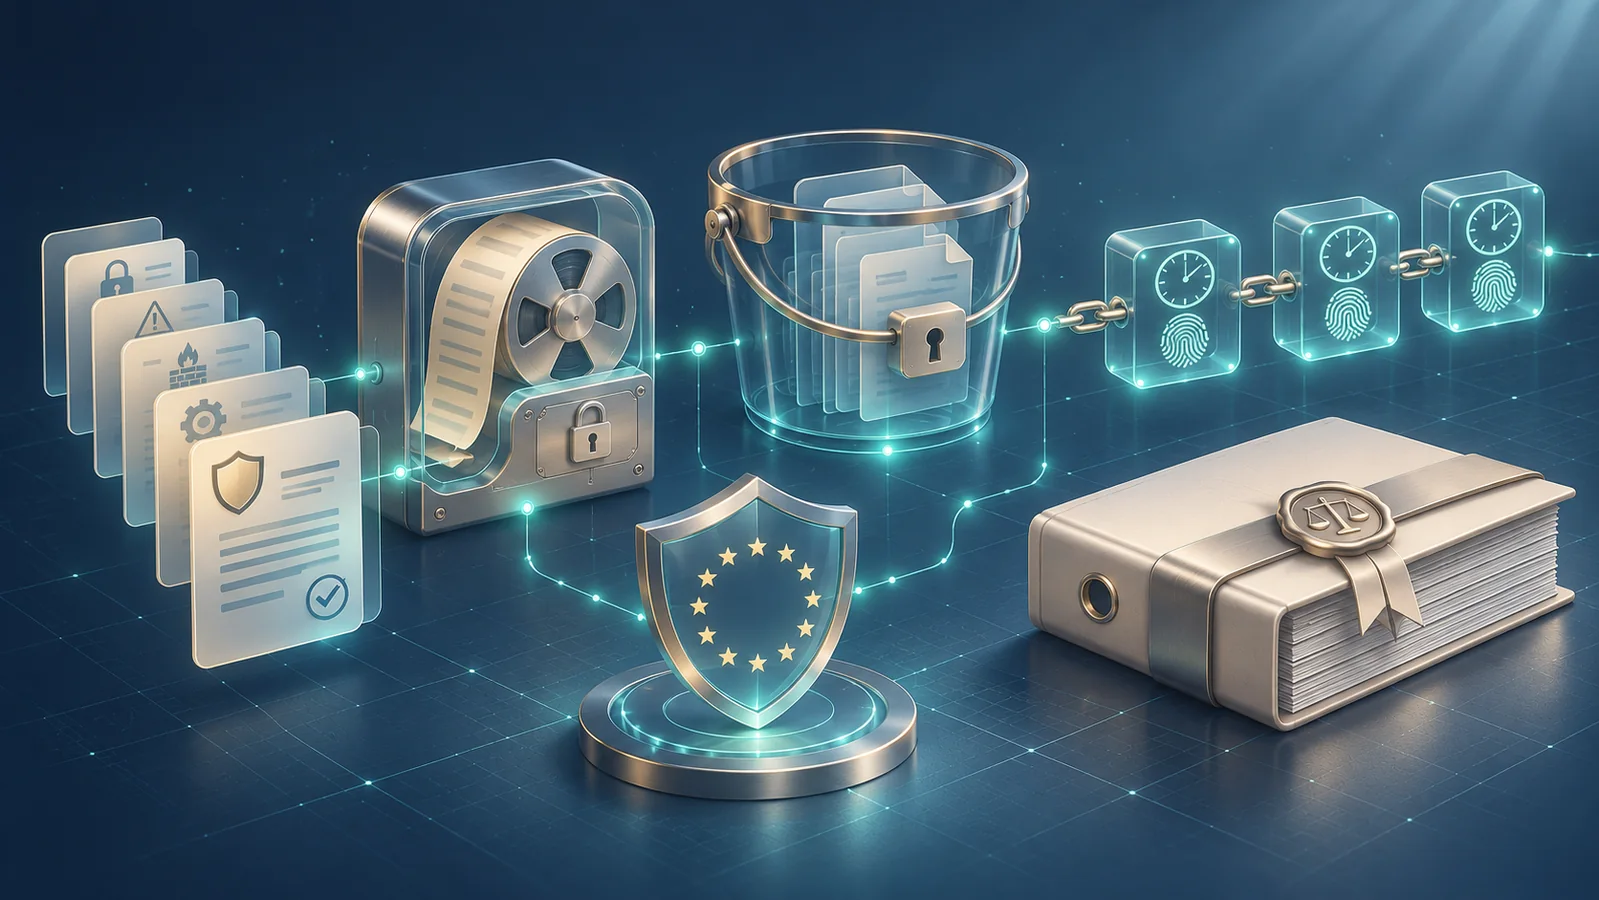
A complete pipeline: creation / collection, source identification (UUID), timestamping via TSA, SHA-256 integrity calculation, WORM storage, sensitivity classification, RBAC access control, retention, periodic hash verification, read-only consultation, certified export for audit, end of retention or legal hold.
Link with forensic incident management
Immutable logs enable exact chronological reconstruction. Qualified timestamps provide irrefutable evidence before authorities. Forensic analysis benefits from a robust chain of custody thanks to digital signatures, facilitating documented corrective actions and dialogue with insurers.
Governance and management accountability
- validation of approved architectures in signed minutes (PDF/A) archived in immutable mode;
- budgetary allocation for WORM and TSA services within the annual plan;
- monthly CISO supervision via electronically signed dashboards;
- certified training for technical teams and executive management.
Pragmatic implementation for SMEs and mid-caps
- map applicable NIS2 obligations;
- define a versioned JSON-LD evidence register via Git;
- assign a data custodian per category;
- automate collection (hash + WORM transmission);
- protect via restrictive IAM and KMS encryption;
- periodically verify integrity;
- regularly test the audit trail.
Limitations that should not be concealed
- pseudo-immutability possible if the source is corrupted at origin;
- GDPR conflict (right to erasure) vs NIS2 retention requiring a documented Legal Hold;
- immutability does not replace prevention; it strengthens the demonstration of controls.
Further reading
Related links:
Read the Challenges article on KARL →